JWT Decoder
Decode a JWT token and inspect its header and payload in a readable format. This tool is useful for debugging authentication flows, checking token claims, and understanding how a JSON Web Token is structured.
Do not paste live production tokens, admin tokens, customer tokens, private keys, or secrets into this tool. Use demo tokens, local test tokens, or tokens with sensitive values removed.
Find this tool useful? Support the project to keep it free!
Buy me a coffeeWhat is JWT Decoder?
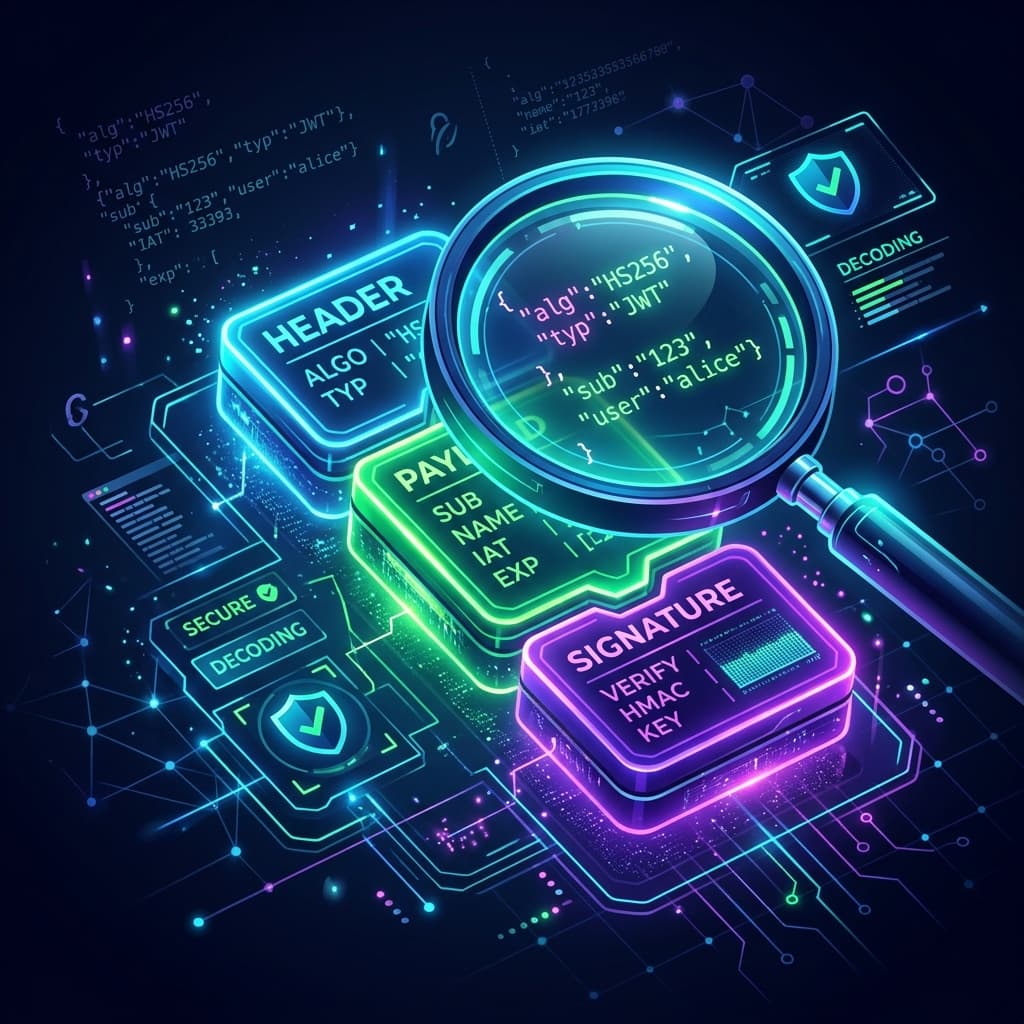
JSON Web Tokens (JWT) are compact strings used to carry claims like user IDs, roles, issuers, audiences, and expiry timestamps between systems. They consist of header, payload, and signature sections separated by dots. This tool decodes the readable parts so you can inspect what a token actually contains.
That is especially useful during authentication debugging. If a user session fails, an API rejects a request, or a token appears expired, decoding the claims quickly helps you see whether the issue is the payload itself, the timestamp window, or a validation rule elsewhere in the stack.
How to Use JWT Decoder
Paste a demo JWT, local test token, or redacted token into the input
Review the decoded header to check the algorithm and token type
Review the decoded payload to inspect claims such as sub, exp, iat, iss, aud, role, and permissions
Check whether the expiration timestamp matches the behavior you are debugging
Use your application or a dedicated verifier when you need to validate the signature
Common Use Cases
- Inspect token payload during login debugging.
- Check whether a token has expired.
- Confirm user role or permission claims.
- Debug frontend/backend authentication mismatch issues.
- Understand JWT structure while learning API authentication.
Example Input and Output
Use safe demo tokens or redacted local test tokens when inspecting JWT structure.
eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJzdWIiOiIxMjM0NTY3ODkwIiwibmFtZSI6IkRlbW8gVXNlciIsImlhdCI6MTUxNjIzOTAyMn0.demo-signatureHeader:
{
"alg": "HS256",
"typ": "JWT"
}
Payload:
{
"sub": "1234567890",
"name": "Demo User",
"iat": 1516239022
}Is It Safe to Decode JWT Tokens Online?
JWT decoding runs in the browser, but tokens can still contain sensitive internal claims or grant access while they are valid. Do not paste live production tokens, admin tokens, customer tokens, private keys, or secrets into any online tool. Use demo tokens, local test tokens, or tokens with sensitive values removed.
Important distinction
Decoding is not verification. A token can decode cleanly and still be invalid because the signature, issuer, audience, or expiration checks fail in your application.
Frequently Asked Questions
What is a JWT decoder?
A JWT decoder reads the Base64URL-encoded header and payload sections of a JSON Web Token and displays them as readable JSON so you can inspect claims and token metadata.
Can this tool verify a JWT signature?
No. This tool decodes the readable JWT sections only. Signature verification requires your application secret, public key, issuer rules, audience rules, and expiration checks, which should not be pasted into a public tool.
Is it safe to decode a JWT online?
Decoding happens locally in the browser, but JWTs can still include sensitive claims or live session access. Do not paste production tokens, admin tokens, customer tokens, private keys, or secrets. Use demo tokens, local test tokens, or redacted values.
What is the difference between decoding and validating a JWT?
Decoding means reading the header and payload. Validation means checking the signature and confirming claims like issuer, audience, and expiration against your application rules.
What is the difference between JWT header and payload?
The header usually describes the token type and signing algorithm. The payload contains claims such as the subject, issuer, audience, issued-at time, expiry time, roles, or permissions.
How do I check when a JWT expires?
Look for the exp claim in the decoded payload. It is usually a Unix timestamp. Compare it with the current time to see whether the token is still inside its expected validity window.
Why does a JWT have three parts?
A JWT normally has three dot-separated parts: header, payload, and signature. The header and payload can be decoded for inspection. The signature is used by the receiving application to verify that the token has not been tampered with.
Why is the payload readable if the token is supposed to be secure?
JWT payloads are Base64URL-encoded, not encrypted. The security comes from validating the signature and claims, not from hiding the payload text.
Security and Auth Workflow
Generate safer credentials, inspect tokens, verify signatures, and compare hash outputs from the same family.
Related Tools
Base64 Encoder/Decoder
Encode text to Base64 or decode Base64 to plain text — with URL-safe mode, auto-detect, and size stats.
JSON Formatter
Format, validate, and beautify JSON instantly — with clear error messages, Tree View, Diff mode, and Schema validation.
JSON Tree Viewer
Visualize JSON data in an interactive tree structure.
HTTP Status Code Reference
Searchable reference for all HTTP status codes — with meaning, common causes, and fix recommendations.
Webhook Tester
Receive, inspect, and debug incoming webhooks in real-time — see headers, body, query params, and method for any HTTP request sent to your unique endpoint.
JSON Decode Online
Decode a JSON-escaped string back to plain text. Unescapes quotes, backslashes, newlines, and Unicode \uXXXX sequences. Works with or without surrounding quotes.
Part of Collections
Posts for This Tool
Broader workflow content that links this tool back into the wider cluster.